A Law Racing Against Machines It Didn't Anticipate
The Digital Personal Data Protection Act, 2023 (the DPDP Act) became law well before autonomous Artificial Intelligence (AI) agents were a mainstream reality, and its November 2025 Rules arrived without meaningfully addressing questions that agentic systems raise. Enforcement in earnest is not slated to begin until May 2027, but the technology it was meant to govern has not been waiting around either. Agentic systems capable of acting on a person's behalf across dozens of services have matured faster than the statute could anticipate, and there is every reason to expect the distance between the two to widen further before the compliance deadline even arrives.
This is not an argument against any particular product or deployment but an observation about architecture. India's consent regime was built for a world of discrete, user-triggered events, and technological advancement is now demanding it to govern something that behaves more like a continuous, self-directing process.
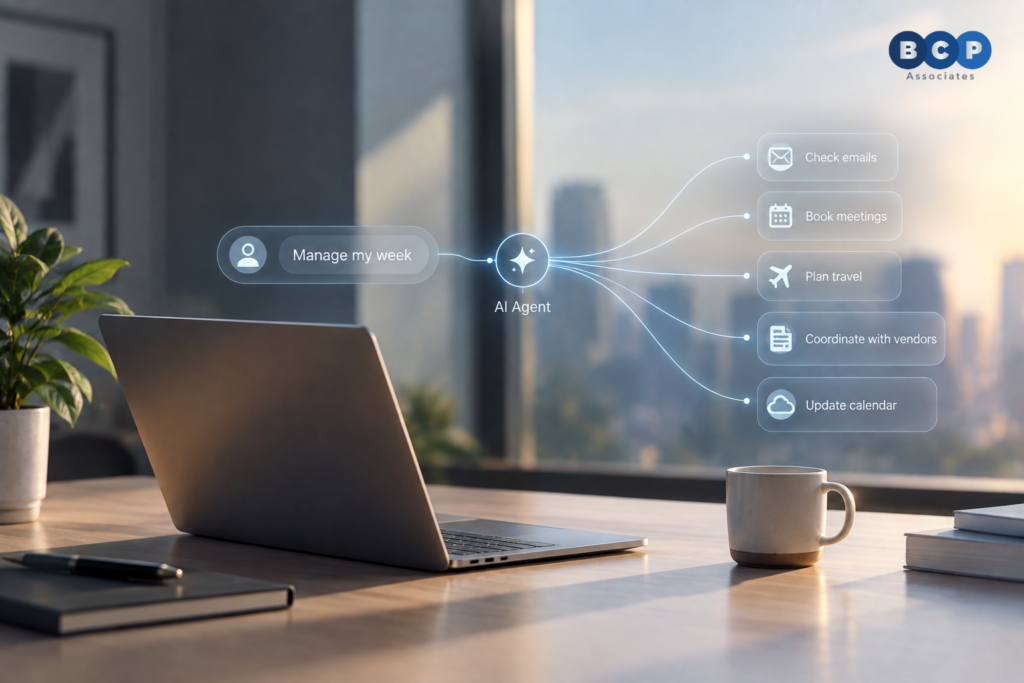
Give a traditional website an instruction and the causal chain is short - you fill a form, click submit, and a fairly predictable piece of processing follows. Autonomous agents break that chain. Tell one to "sort out my week" or "handle the vendor onboarding," and what follows may be a long, unpredictable sequence of touches: third-party lookups, data shared across systems, messages sent, even commitments entered into, none of which were individually authorised, all of it downstream of one sentence.
That is the core design feature worth naming: delegation. And it is precisely what the DPDP Act's drafters did not build for. It’s vocabulary - informed, specific, free, unambiguous, tied to affirmative action - presumes a person consciously approving a bounded activity. It does not have an appropriate language for a single green light that unlocks an open-ended, evolving chain of downstream events.
Multiple fiduciaries, one authorisation:
The DPDP Act treats each data fiduciary as independently accountable for notice and consent. But an autonomous agent may pull in a dozen platforms on a user's behalf, each arguably a fiduciary in its own right — and the law offers little on how any of them discharge that duty when the only "yes" ever given went to the orchestrating AI, not to them.
Data belonging to people who never logged in
An agent managing your inbox is also touching the data of everyone who emailed you. One coordinating an event is processing every invitee's details. One assisting at work may be handling colleagues' and clients' information. Whether the DPDP Act's personal-or-domestic carve-out rescues any of this is highly fact-specific and gets murkier the moment commercial intermediaries are involved. Where the exemption does not apply, getting consent from these incidental parties inside an automated pipeline is often simply not practical.
A withdrawal right with nothing left to withdraw from
The law requires that pulling consent be no harder than giving it. But autonomous systems collapse the gap between "yes" and "done" by the time someone thinks to withdraw, data may already be shared, a transaction completed, a message sent to a third party. The window in which revocation still matters can shrink to almost nothing.
Preferences the system built rather than found
The most conceptually awkward tension: sophisticated agents do not just execute instructions; they model you and act on predicted wants. That inverts the DPDP Act's core assumption — that a stable, pre-existing intention is what authorises processing in the first place. When the system is partly responsible for shaping the preference, it then acts on, calling the result "consent" starts to feel circular. Whether adaptive defaults and recommendation logic quietly erode the freedom element of consent is a question the DPDP framework has not really engaged with yet, though it is likely to matter more, not less, as these systems get more capable.
Run any of the statute's core requirements against an actual agent instruction and the fit is uncomfortable.
Specificity assumes a defined purpose up front. "Manage my inbox" does not tell anyone which contacts get touched, what gets inferred, or what gets sent — much of that gets decided on the fly as the agent encounters new situations, which sits badly with a consent regime built around bounded purposes.
Being informed assumes the person knows what data will move and why. Two things break this for agentic systems: the categories of data involved often are not knowable in advance — they surface only as execution unfolds — and purposes drift, since information gathered for one task can end up reused, retained, or passed along by parties nobody could have named when the process began.
Freedom assumes consent is not a precondition dressed up as a choice. Many agentic tools are functionally unusable unless you accept profiling, inference, or wide third-party sharing that isn't strictly needed for the task at hand — and once several downstream services start layering their own conditions on top, the "freely given" label gets harder to defend.
Absent clearer rules, the strongest available position is over-disclosure done well, not blanket terms-of-service acceptance. A notice that actually holds up should spell out which categories of data are in scope, which third parties and fiduciaries might get pulled in, and the realistic range of purposes the system might serve. Consent taken against that kind of concrete map is a meaningfully stronger footing than a generic sign-off.
Worth layering on top:
● Just-in-time notices that fire when the system is about to do something materially new;
● Authorisation scoped to defined contexts rather than open-ended permission; and
● Dashboards, logs, and audit trails so users can actually see what has been done in their name.
Consent managers, i.e. the intermediaries the DPDP framework already contemplates for recording and relaying consent, could eventually help coordinate this across multiple fiduciaries, though whether they can keep pace with agentic speed is still an open question.
None of this is a full fix, though, and it 'is worth being honest about the ceiling. Push a disclosure broad enough to cover every conceivable future action, and it starts to resemble the blanket consent the DPDP Act was written to prevent - the more ground it covers, the less specific it can be. It also does not touch the third-party problem, since notifying your primary user says nothing to the people whose data gets swept in incidentally. And a notice frozen at day one ages badly against a system whose processing logic keeps evolving.
The Regulatory Gap
What is missing is not better drafting by individual companies, but the rulemaking that actually engages with how these systems work: workable standards for scoped authorisation across chains of fiduciaries; a real answer for third-party data swept up incidentally; allocation of responsibility when one AI system is instructing another; and a definition of "meaningful consent" that still holds when the entire human contribution was a single opening instruction.
For any business running autonomous AI today, the honest framing is that consent is not a solved compliance checkbox, but a live risk to be actively managed. Thorough disclosure, layered consent design, documented purpose-mapping, and real transparency tooling are the best tools currently on the table, and they meaningfully reduce exposure, but they don't dissolve the underlying mismatch between a law written for single events and a technology built to chain them indefinitely. The businesses in the best position when enforcement finally lands in 2027 will be the ones that mapped these gaps early and built toward them, rather than waiting for the regulator to draw the lines first.
Related Article: AI-Generated Content in India: Key Considerations Under the IT Rules - BCP Associates , 11 May 2026